U.S. Senate leadership is negotiating a bipartisan regulatory bill that would impose legal liability on developers of the most powerful AI models to mitigate significant risks. The core concept is a “duty of care”—a safety obligation requiring developers to prevent catastrophic risks when designing their products.
The proposals under discussion include provisions that would allow the U.S. government to block the release of certain AI models it deems unsafe. However, procedures allowing companies to challenge the government’s decisions in federal court are also being considered, and the scope of the government’s authority and the criteria for its determinations have not yet been agreed upon.
At this point, the bill’s wording has not been finalized or formally introduced in Congress. Since this is a draft proposal based on information disclosed by Senate staff and negotiators, You shouldn't assume the law will take effect immediately.
| A Proposal to Make Safety Recommendations a Legal Obligation
Until now, major AI companies have managed the risks associated with high-performance models primarily through their own safety policies, external evaluations, and voluntary cooperation with the government. The Senate bill currently under discussion The key difference lies in the fact that this is an attempt to transform it from a corporate choice into a legal obligation.
If safety obligations are introduced, developers will likely be required to provide evidence that they designed their models and deployment processes to mitigate known significant risks. This goes beyond simply declaring that they prioritize safety, Whether pre-launch assessments, risk mitigation measures, and incident response systems were actually implemented may be subject to evaluation.
However, it has not yet been disclosed at what scale and performance level the requirement applies, nor what measures developers must take to be considered to have fulfilled their responsibilities. If these criteria are vague, it will create significant uncertainty for companies; if they are too narrow, the most dangerous models may not be properly identified.
| The government's authority to restrict the release of models
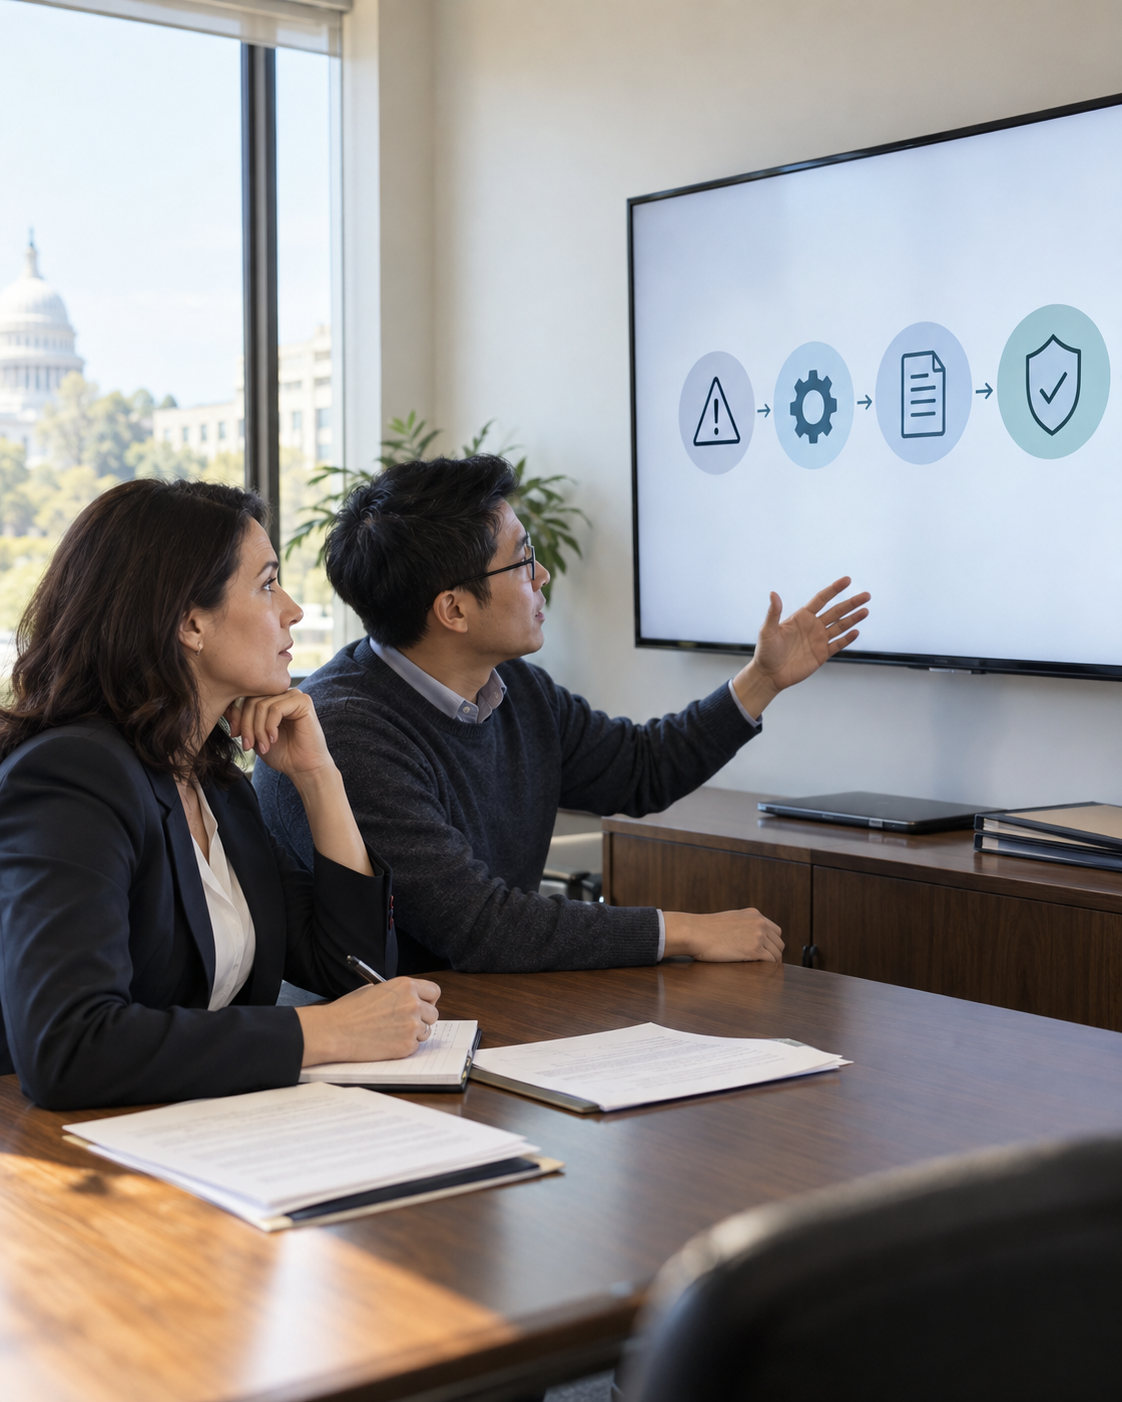
The proposal is considering a provision that would give the U.S. government the authority to block the release of certain AI models if it deems them unsafe. If this is actually included, The system will prioritize risk management before launch over post-incident penalties.
At the same time, measures are being discussed that would allow developers to challenge the government’s decision in federal court. This can be seen as a mechanism designed to avoid a system where the government makes unilateral decisions and to balance urgent safety measures with companies’ procedural rights.
The biggest issue is the blocking criteria. The bill’s effectiveness will depend on factors such as whether the restrictions are limited to the mere possibility that a model could generate harmful information, whether specific capabilities must be verified through actual evaluation, and whether the model can be re-evaluated after risk mitigation measures are implemented.
| Independent verification by national research institutions
Senator Amy Klobuchar stated that she is discussing a plan to require developers to validate and test their models in collaboration with government experts. Senator Maria Cantwell also expressed the view that the most powerful AI models should be evaluated by scientists and experts at U.S. national laboratories.
The review covers capabilities that could facilitate sophisticated cyberattacks or increase major biological or nuclear risks. The key is a system in which public research institutions take on a separate verification role, rather than relying solely on internal corporate evaluations.
For this system to work, national research institutes must determine the extent to which they will have access to models and evaluation data. They must be able to reach independent conclusions while protecting corporate trade secrets and security information, and they will also need specialized personnel and computational resources to test rapidly evolving models.
| Conflicts Between Federal Standards and State Laws
The measures under discussion may include provisions that limit the enforcement of state laws addressing specific high-risk AI issues. This is referred to as the primacy of federal law or the preemption of state law. While this could establish a single national standard, it has sparked debate over whether it might prevent states from implementing stronger safeguards.
From a company's perspective, this reduces the burden of having to follow different rules each week. On the other hand, If federal standards are weak or enforcement is delayed, it could limit the state government's ability to take the lead in responding. So, a key point of negotiation is which high-risk areas the federal government will take on and to what extent state governments will retain their authority.
|
Topics for Discussion |
Current Direction |
Points that have not yet been decided |
|
Safety Obligations |
Calling on cutting-edge AI developers to consider mitigating catastrophic risks |
Application Criteria and Scope of Liability |
|
Release Restrictions |
Government Considers Authority to Block the Release of Certain Risk Models |
Blocking Requirements and Responsible Agencies |
|
Judicial Review |
Review to allow companies to challenge government decisions in federal court |
Adjudication Speed and Standard of Proof |
|
External Evaluation |
Experts from a National Research Institute to Conduct Model Testing |
Access Permissions and Evaluation Methods |
|
Preemption of State Law |
Review of State Law Enforcement Restrictions Regarding Risks Associated with Certain High-Performance Models |
Scope of Restrictions and Exceptions |
| The Context Behind the Bipartisan Discussions
Senate Majority Leader John Thune, Senate Commerce Committee Chairman Ted Cruz, and Amy Klobuchar, who is representing the Democrats in the negotiations, are involved in the talks. Maria Cantwell, the Democratic ranking member of the Commerce Committee, is also contributing her views to the discussions on the bill.
Cruz announced that he is working with Klobuchar and Thune on a bill to address catastrophic risks related to biological and nuclear threats. Klobuchar emphasized the need for government oversight and expert verification of high-risk AI models, while Cantwell stated that the National Laboratories should test capabilities related to cyber, biological, and nuclear threats.
The fact that lawmakers from different political parties are participating in the same discussion lends momentum to the bill. However, Bipartisan participation does not necessarily mean agreement on the specific provisions. Differences in position remain regarding the government's authority to block content, restrictions under state law, and the scope of corporate liability.
| Impact on Google, Anthropic, and OpenAI
Reuters reported that these discussions focus on AI models with the most advanced capabilities, citing Google, Anthropic, and OpenAI as major U.S. developers. Depending on the criteria set forth in the final legislation, other major developers could also be subject to the regulations, but neither the list of companies nor the performance standards has been finalized yet.
If the law is enacted, the launch process for high-performance models may require additional steps, such as external testing, document submission, and risk mitigation verification. While this could slow down development and impact launch schedules, it is also expected to help align the varying safety standards of different companies with a common minimum standard.
We also need to assess the impact on small and medium-sized enterprises and open-source developers. If regulations are applied broadly without clear criteria—such as computational load or model capabilities—they could place a greater burden on developers, who have fewer resources to respond than large companies. Conversely, if we focus narrowly on only the most cutting-edge models, the direct impact on general AI services may be limited.
| Chances of Passing and What to Watch for Going Forward
The legislative timeline is tight. As of the time of the Reuters report, the House has only one week left in its session before the November 3 midterm elections, while the Senate has about three weeks remaining. Even if a negotiated agreement is drafted into a formal bill, it will take time to go through committee review, pass both chambers, and be signed by the president.
What is currently confirmed is that key members of the Senate are discussing a bipartisan bill to address the significant risks posed by advanced AI. Safety obligations, government launch restrictions, federal court review, evaluations by national research institutes, and certain state law restrictions are all elements currently under negotiation and are not final provisions.
Going forward, we need to verify the official bill number and text, the performance standards for the entities subject to the law, the legal definition of catastrophic risk, the government’s decision-making process, and the scope of state government authority. Only once this information is made public will we be able to determine whether these discussions will lead to substantive safety regulations or remain at the stage of political consensus.
Tags
#U.S. Senate #AI Regulation #AI Safety #High-Performance AI #FrontierAI #OpenAI #Anthropic #Google #Safety Obligations #National Research Institute #Cybersecurity #AIPolicy