The British fintech company Revolut has confirmed that it was tricked by a fraudulent information request disguised as a legitimate request from a government agency and disclosed customers' sensitive information to an unauthorized third party. This wasn't an incident where an attacker directly breached Revolut's core systems; rather, it was an incident where the procedure for verifying information requests was compromised by a deception.
A Revolut spokesperson told Reuters that the fraudulent requests were sent from legitimate email domains belonging to actual government agencies. The spokesperson stated that after discovering the incident, the company blocked the relevant addresses and notified the relevant government agencies, law enforcement, and personal data and financial regulatory authorities.
The exact number of people affected has not been disclosed. Although the company stated that its systems and customer funds were not compromised, the fact that personal information that could be used for identity verification was leaked means the potential for harm cannot be taken lightly.
| An Incident Caused by a Failure in Process Verification Rather Than a Hacking Attack
The crux of this incident isn't that an outsider hacked into the customer database. Rather, Revolut employees or the relevant processing system disclosed information in response to a request they believed came from a government agency, only to later discover that the request was fraudulent.
Financial institutions must respond to lawful requests for information from law enforcement or regulatory agencies. The problem is Just because the sender's domain appears to be legitimate does not automatically guarantee the requester's identity or legal authority.
Based solely on the Reuters report, it remains unclear whether government agency accounts were compromised, whether the email transmission path was tampered with, or whether the legitimate domain was exploited in some other way. That is why we should not jump to conclusions about the specific attack methods.
| What information was exposed?
According to a TechCrunch report cited by Reuters, the leaked information included customers' dates of birth, mailing addresses, email addresses, and phone numbers. It was also reported that copies of some identification documents, such as passports and driver's licenses, were compromised.
However, Revolut did not disclose to Reuters the exact number of affected individuals or the specific types of information exposed for each customer. There is also no evidence yet to suggest that the same type of information was leaked for all affected individuals.
Even if your account password or funds haven't been directly stolen, combining various pieces of personal information can be exploited for sophisticated impersonation and phishing scams. In particular, since copies of identification documents are harder to update than general contact information, long-term risk management is necessary.
| Why You Shouldn't Trust Only Legitimate Domains
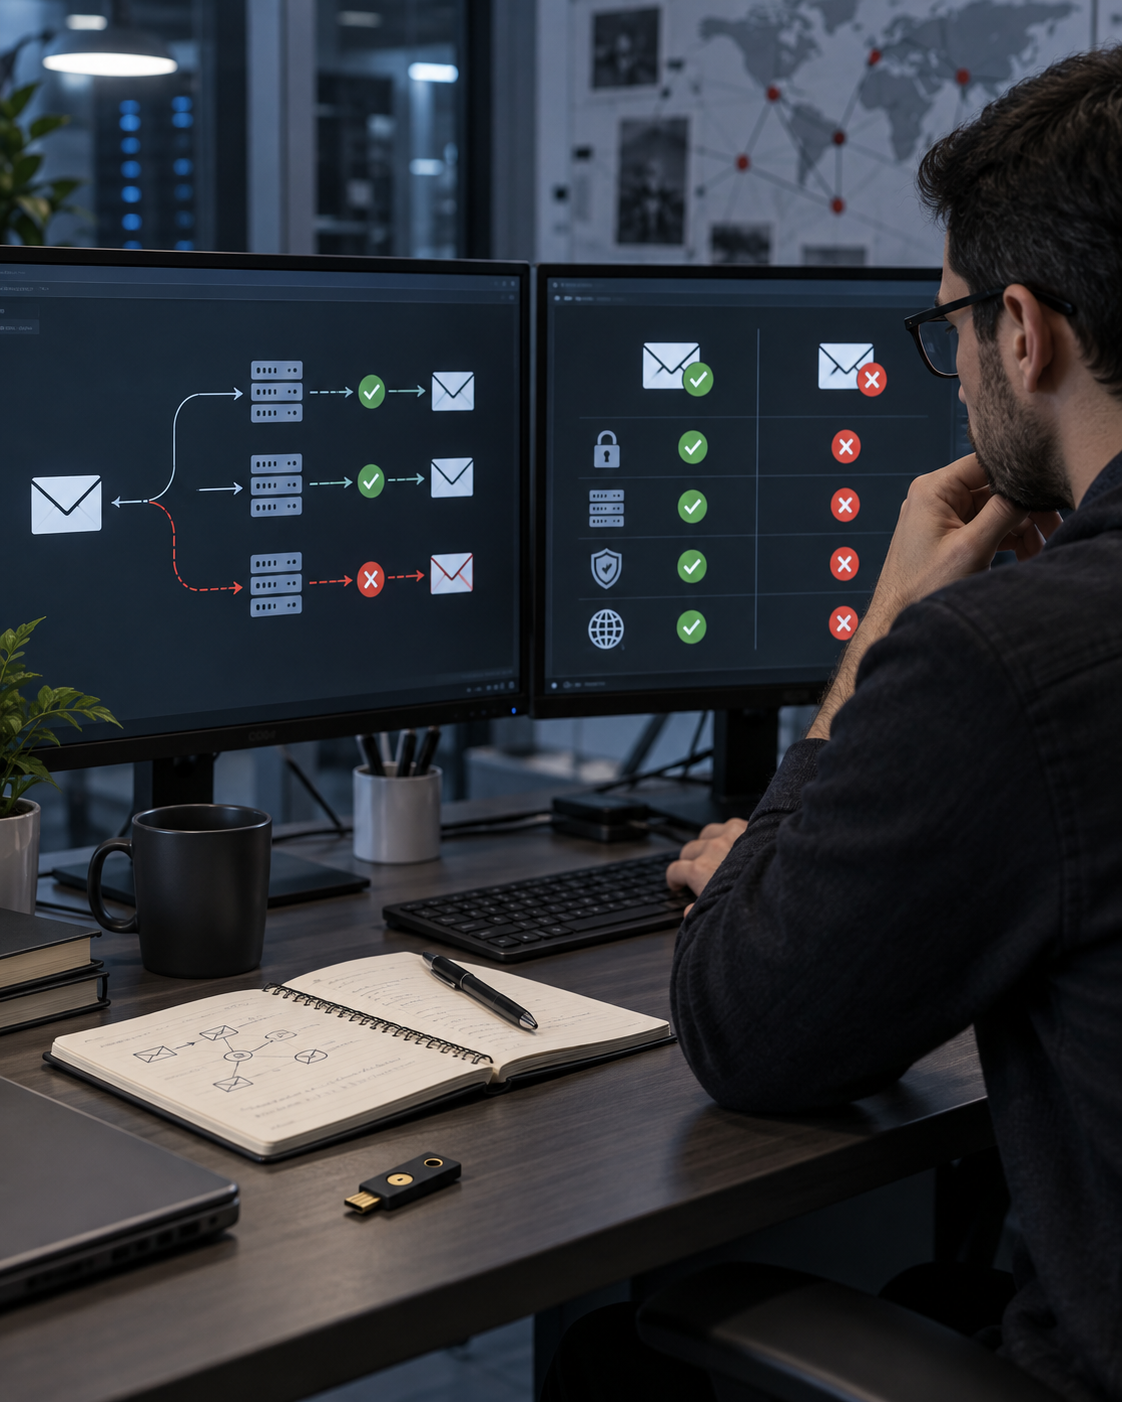
If a company’s request verification process relies too heavily on email addresses or domains, the entire defense system could collapse if even a single trusted account is compromised. Sender information that appears official is just one verification factor—it is not definitive proof.
Before providing sensitive information, you must use an independent communication channel to double-check that the request number, legal basis, identity of the responsible agency and the person in charge, and the scope of the request all match. That's why we need a procedure to verify the information through the organization's official channels, rather than relying on the contact information provided in the original email.
Rather than having one person receive a request and immediately send out the materials, It's safer to have dual approval from the legal and privacy officers and to minimize the scope. Even if a request is legitimate, providing only the necessary customer information and items is the way to minimize the scope of the damage.
| The Scope of the Statement That Customer Funds Are Safe
Revolut stated that its systems and customer funds were not affected. This can be interpreted to mean that there is no evidence that account balances or the transaction system were directly compromised by this incident.
However, that doesn't mean there was no breach of personal information. Attackers who have obtained contact and identification information could later launch a secondary attack by impersonating Revolut or a government agency to request additional information.
Therefore, the company goes beyond simply explaining that there has been no financial loss, It is necessary to notify each customer individually about what specific information of theirs has been exposed and to provide measures to help detect identity theft. It's because customers need to understand their own risk tolerance in order to respond appropriately.
| Revolut's Initial Response and Remaining Questions
The company stated that it blocked the address in question immediately after discovering the incident and notified the relevant agencies and regulatory authorities. This was the first step taken to prevent further requests and to facilitate an official investigation.
However, It has not been disclosed when the incident began, how long it lasted, how many requests were processed, or at which stage of the internal verification process the failure occurred. We need this information to assess the extent of the damage.
There have also been reports that Revolut is preparing for a potential IPO and aiming for a valuation of up to $200 billion. As a major financial platform, it faces an even greater burden to prove to the market its ability to protect personal information and comply with regulations.
| Security Challenges Left by This Incident
This incident shows that financial security isn't limited to firewalls and encryption alone. Since requests that mimic legitimate business procedures can also serve as channels for data breaches, the security model must include both people and the approval process.
According to the company, what has been confirmed so far is that sensitive information was provided to a third party through a fraudulent government request, and that the incident had no impact on the company's systems or funds. The exact number of victims, the method of the attack, and the scope of the data breach have not yet been determined.
Going forward, we will need to review the findings of the regulatory agency’s investigation, the details of the notifications sent to victims, and the additional verification procedures Revolut will implement. The final assessment of the incident will depend on how much customer data was compromised and whether subsequent misuse was prevented.
Tags
#Revolut #Data Breach #DataBreach #FintechSecurity #Information Security #Social Engineering #Phishing #ID Leak #Financial Security #Privacy #Cybersecurity #Security Incident


