If the private keys and seed phrases hadn't been compromised, would this incident have been a minor issue?
The security incident disclosed by SafePal was not a case where the cryptocurrency wallet itself was hacked. However, given that order information—including who purchased the hardware wallet, which product was purchased, and where it was shipped—was exposed to the public, this cannot be taken lightly.
SafePal, a cryptocurrency wallet provider, reported on August 16, 2026, that a privilege escalation vulnerability in its order tracking feature resulted in approximately 39,798 peopleThe company announced that there had been an unauthorized access incident involving customer information. The Reuters report was published at 1:03 a.m. on August 17, Korea Standard Time.
The key point of this incident is not that the encryption key used to access the assets was directly compromised, but rather that Methods an attacker can use to sophisticatedly deceive a victim Ingredients of TrustI heard that... Yes.
| Authorization Vulnerability in the Order Tracking Feature
According to SafePal, the issue was discovered in the order tracking feature of a plugin linked to customer order information. Under certain conditions, the authorization checks did not function properly, allowing one customer to view another customer's order information.
It is important to distinguish between authentication and authorization here.
|
Category |
Items to Verify |
Connection to this incident |
|
Certification |
Verify the identity of the person who logged in |
Steps for identifying an account or user |
|
Approval |
Verify that the person has permission to access that information |
Steps to prevent access to other customers' order information |
Simply put, A situation where only the user's own orders should have been displayed on the package tracking screen, but due to a misconfigured permission boundary, other customers' order information could also be accessed.Hey.
However, SafePal did not disclose the specific implementation details of the vulnerability or the exact time when the external access first began. The disclosed From March 2, 2025, to April 11, 2026That range refers to the dates when affected customers placed their orders, not the duration of the attack.
| Disclosed Information and Undisclosed Information
The information that was accessed by unauthorized external parties in this incident includes Includes items that can link a customer's identity to a purchaseOkay.
|
Information for which external access has been confirmed |
Information disclosed by SafePal stating that it was not involved in the incident |
|
Name |
Seed Phrase |
|
Email Address |
Private Key |
|
Shipping Address |
Wallet Passwords and Other Wallet Credentials |
|
Phone number |
Bank Account Information |
|
Purchase and Order Details |
Payment Card Number |
|
Government-Issued ID Number |
SafePal stated that it found no evidence that the incident itself had granted anyone access to the wallet or funds.
Therefore, it is inaccurate to say that the customer's cryptocurrency was directly stolen. The correct way to put it is Unauthorized access occurred to the order and personal information of 39,798 peopleThat's it.
That doesn't mean the risk has gone away, though. Unlike typical spam lists, where only names and contact information are leaked, this data includes the fact that the victims actually purchased SafePal products, along with their shipping information.
| The Harm Caused by the Disclosure of Order Information
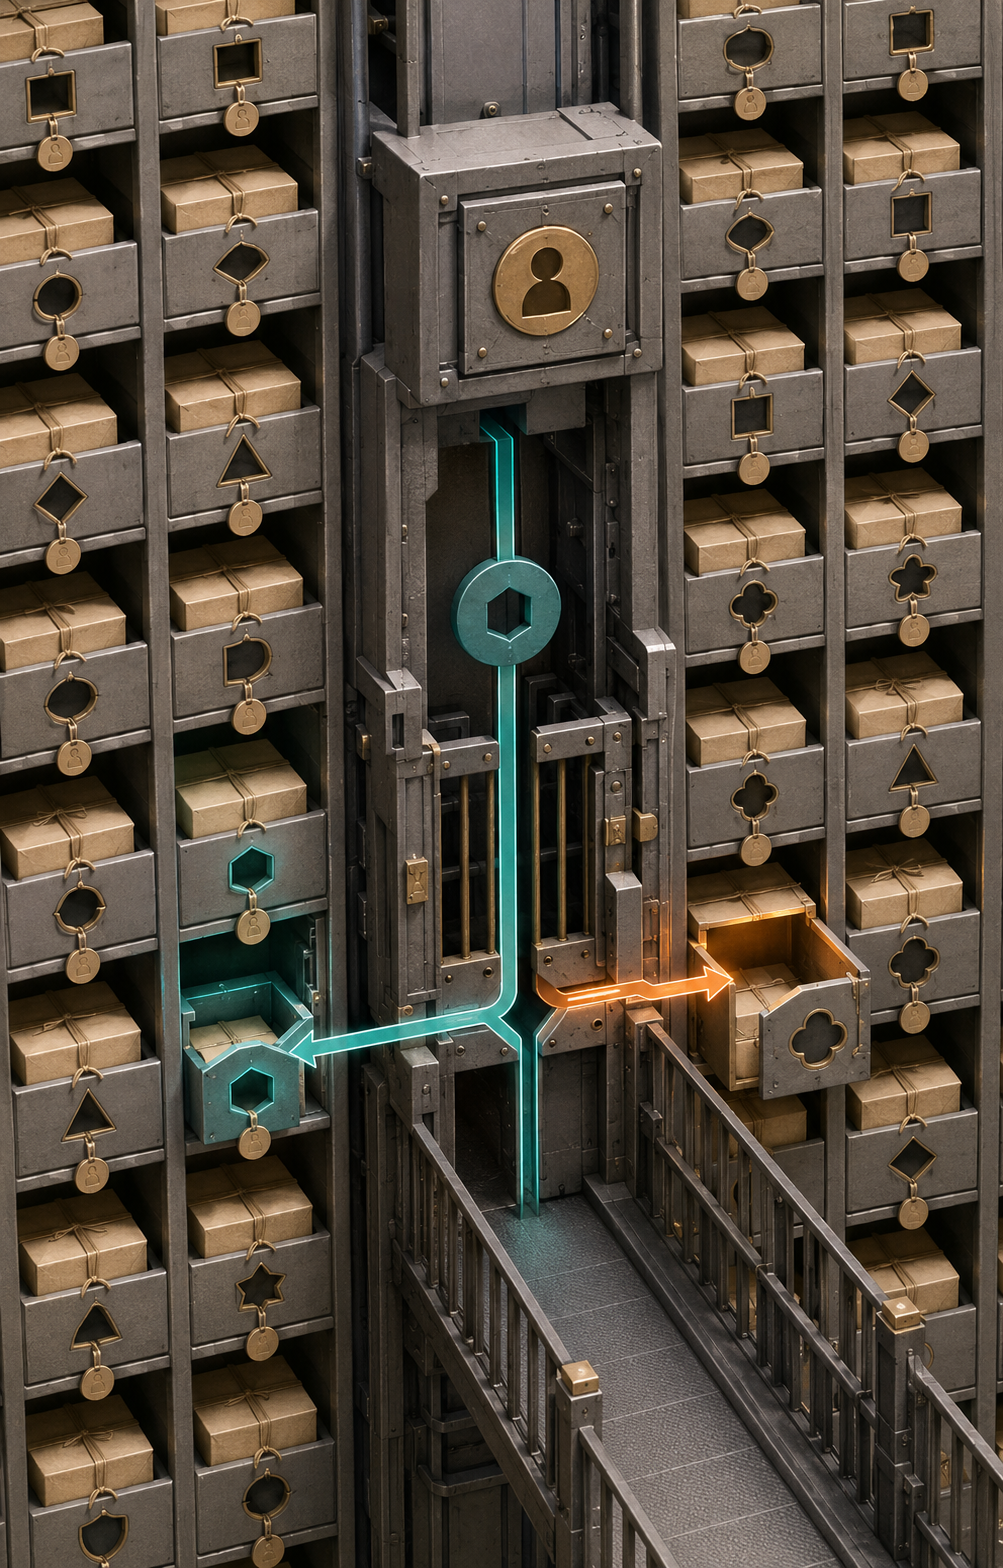
Random phishing messages often seem relatively awkward because the sender isn’t familiar with the user’s situation. On the other hand, if an attacker knows the user’s name, phone number, address, and purchase and order history, it becomes easier to create a message that appears to be from actual customer support.
For example, an attacker might cite reasons such as a product exchange, refund, security check, or firmware update. If the message contains some information related to an actual order, It becomes more likely that the victim will conclude, “Since they know I made a purchase, this must really be SafePal.”
Targeted phishing is becoming increasingly dangerous for the following reasons.
Extracting Actual SafePal Customers Using Leaked Order Information
Sending personalized phone calls, text messages, emails, and mail using names and purchase history
Tricking users into visiting a fake customer support page under the pretext of a refund or update
In the final step, it asks for key information such as the seed phrase, private key, and wallet password
Although the seed phrase wasn't directly exposed in this incident, if an attacker tricks a user into entering that information themselves, it could lead to financial loss. Phishing is the link between personal data breaches and wallet theftThat's basically it.
The fact that SafePal announced it had identified and blocked more than 30 fake websites and phishing links linked to this incident also shows that the risk was not merely a possibility.
| Security of Hardware Wallets
A hardware wallet is a device that stores private keys on a device disconnected from the internet, thereby reducing the online attack surface. However, not every step—from ordering the product and receiving it to requesting support—takes place entirely within the hardware wallet itself.
In practice, the service operates as a structure consisting of multiple interconnected systems.
|
Service Areas |
Information Covered |
Key Risks |
|
Wallet Devices and Apps |
Private keys, signatures, and wallet access information |
Device and App Vulnerabilities, Credential Theft |
|
Online Sales System |
Name, Contact Information, Purchase History |
Personal Information Leaks, Account Misuse |
|
Order Tracking Feature |
Order Number, Shipping Status, Order Information |
Identification of Incorrect Permissions, Information Exposure |
|
Logistics and Delivery Partners |
Recipient, Address, Contact Information |
Third-Party System Breaches, Supply Chain Risks |
|
Customer Support Channels |
Inquiry Details, Order Confirmation Information |
Impersonation, Social Engineering Attacks |
Even if the wallet's encryption technology is secure, if personal information is leaked from the sales site or the shipping system, an attacker can find out who owns the wallet. It's similar to how, even if you use the most secure safe, new risks arise if the shipping list—which lists the safe's owner and location—is exposed.
That's why cryptocurrency security isn't just about protecting private keys. It extends from product purchase to shipping, updates, and customer support— Overall Service BoundariesWe need to look at these together.
| Vulnerability Fixes and Shorter Retention Periods
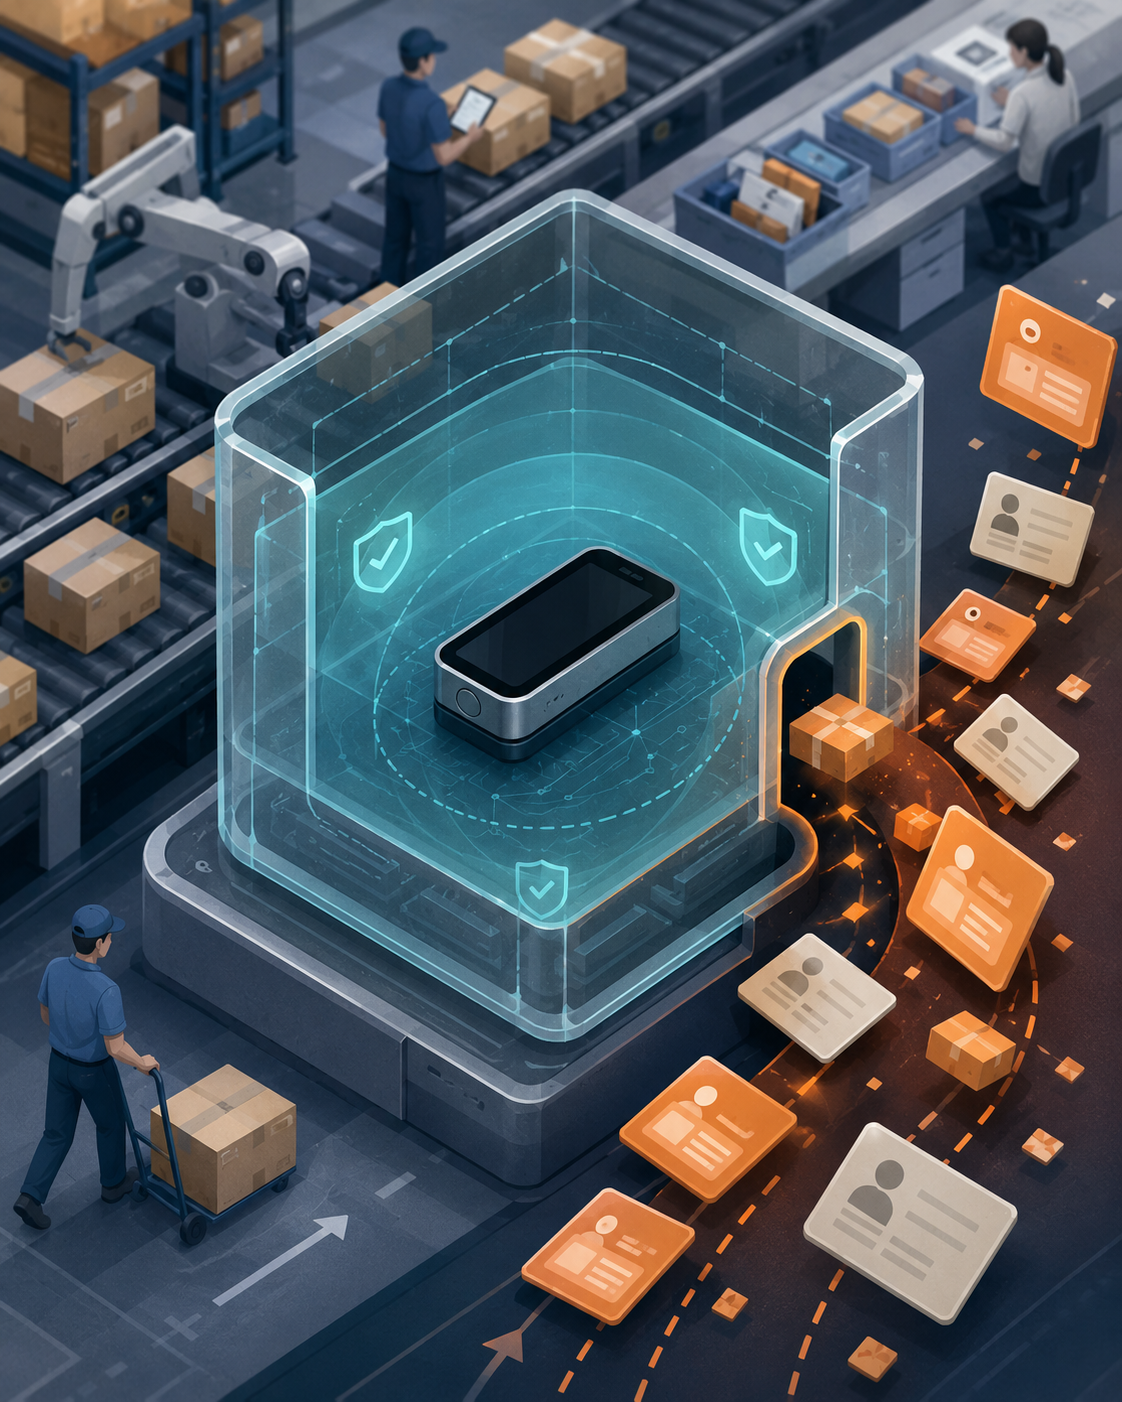
The response measures announced by SafePal are as follows.
Fixed the vulnerability in question and implemented additional security controls
Announced plans to have an independent external security firm review the fixes and the entire order processing system
The retention period for personal information in the relevant order processing environment, within the scope of legal requirements, 90 daysReduce to
Send individual emails to affected customers and operate a dedicated support channel
Check whether the problem has spread further to the systems of logistics and order fulfillment partners
Fake websites and phishing links related to the incident 30 or more Block
Among these measures, the decision to reduce the retention period to 90 days is particularly noteworthy. This is because the longer a company retains personal information, the greater the number of past customers who could be affected by a single data breach.
Storing information only for as long as necessary Data MinimizationAlthough it is not a technology that prevents intrusions themselves, it serves as an important defense mechanism for minimizing the scope of damage when an incident occurs.
However, even if you change your retention policy and fix vulnerabilities, information that has already been accessed from outside the system isn't automatically retrieved. We will need to continue monitoring subsequent announcements regarding the results of the independent security review and whether there has been any additional damage.
| Guidelines for Affected Customers
On August 16, SafePal notified affected customers that security@safepal.com They stated that they had sent individual notification emails to the addresses on file. However, since the sender's address could be spoofed to look similar, you should not verify it by clicking the link in the email directly.
Based on the official guidelines, the following principles are important.
Do not respond if anyone requests your seed phrase, private key, or wallet password via email, text message, phone call, or mail. This is because SafePal has stated that it never requests this information through any channel.
Do not click on links or scan QR codes in unexpected messages.
To access the official website, type the URL directly into your browser rather than clicking on search ads or links you've been sent.
If you receive a message claiming to offer refunds, firmware updates, replacement device shipments, or emergency security checks, verify separately through official channels first to confirm whether it is true.
Report any suspicious calls, messages, or websites through the dedicated support channels listed directly on the official SafePal website.
SafePal explained that if only your order information was affected and you haven't entered your seed phrase or private key anywhere else, there is no need to transfer your assets solely because of this incident.
Conversely, if you have already provided your critical wallet information to a suspicious site or in response to a suspicious contact, you should not assume that the wallet is still secure. Do not respond to any further communications, and immediately check the official website—not any links—for guidance on how to respond to a security breach.
| Data Retention Policies from a Corporate Perspective
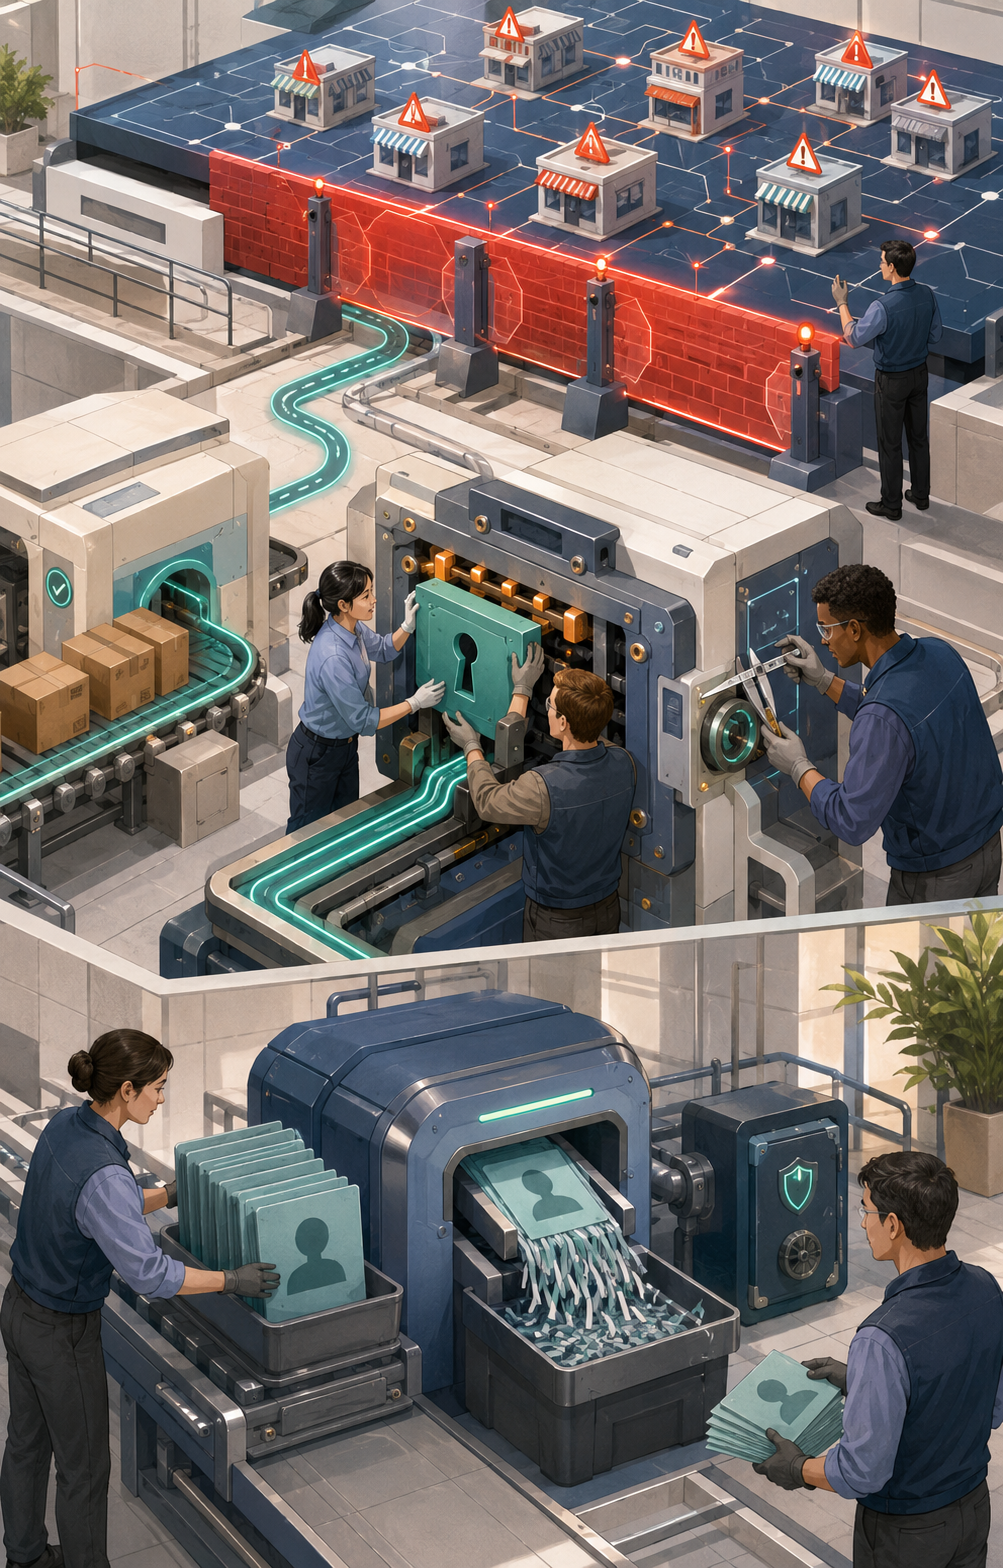
This incident demonstrates that even security and cryptocurrency companies can face risks in their operating systems outside of their core products.
First, verifying permissions is just as important as checking whether a user is logged in. Even if a user has logged in successfully, you must verify with every request that they can only view orders they are authorized to see.
Second, e-commerce and logistics plugins must be managed with the same level of care as core systems. As more external plugins and partners are connected, it is necessary to continuously monitor data flow paths and access permissions.
Third, rather than continuing to accumulate personal information simply because it might be useful someday, it should be retained only for the minimum period required by law and for customer support. This is because past data that isn’t stored cannot be leaked even in the event of a data breach.
Fourth, incident response doesn’t end with patching vulnerabilities. We must identify and block impersonation sites and phishing campaigns that exploit leaked information, and provide official verification channels so that customers can distinguish genuine notifications from fraudulent ones.
| Points that have not yet been confirmed
Although SafePal's public statement confirmed the basic scope of the incident and the response measures taken, not all technical details have been revealed.
It has not been disclosed when the privilege escalation vulnerability first entered the system.
The date when the unauthorized external access first occurred and its duration are unknown.
It has not been disclosed whether the information was accessed by one or multiple parties, or how it was collected.
It is unclear to what extent the exposed information was copied or shared with third parties.
Since the review by an independent security firm is still in progress, the final evaluation results for the entire order processing system have not yet been released.
Therefore, while we should not exaggerate the extent of the damage beyond what has been publicly disclosed, we should also not downplay the risk simply because the private key was not directly exposed. We need to monitor the follow-up investigation and any further announcements.
| Key Takeaways from This Incident
There is no evidence that private keys or seed phrases from wallets were directly leaked in the SafePal incident. However, Unauthorized external access occurred to order information containing the names, contact information, shipping addresses, and purchase history of approximately 39,798 people.
This information alone isn't enough to access your wallet. Instead, it can be used by an attacker to identify real customers, pose as an official employee who knows the order details, and trick you into a fake refund or update process.
Ultimately, this accident was Even if the wallet itself isn't compromised, personal information surrounding the wallet can become a target for attack.This demonstrates that what matters in digital asset security isn't just strong encryption, but the entire framework—including minimizing the data left behind during the purchase, delivery, and support processes, as well as the habit of being suspicious of unexpected contact.
Thank you for reading!
References
#SafePal #SafePal #Data Breach #DataBreach #Cybersecurity #Hardware Wallet #Cryptocurrency Wallet #Phishing #Information Security #Security Incident
Check out our other posts, too!
# Category: Bulletin Board
After we introduced an AI factory, things started to...
https://m.blog.naver.com/jorimisdelicious/224368831067
[Honest Analysis] All talk and no action...
https://m.blog.naver.com/jorimisdelicious/224357697564
[Honest Review] Without any sponsorship...
https://m.blog.naver.com/jorimisdelicious/224355949839
[Don't Miss Out] Quality of Life ...
https://m.blog.naver.com/jorimisdelicious/224354757973
# Category: AI Models and Services
Anthropic Unveils Blueprint for Claude, an AI Agent for Retailers Designed for Shopping and Sales
https://m.blog.naver.com/jorimisdelicious/224400142277
OpenAI Astra Rated 'Critical' for Cyber Capabilities… First Model to Receive Highest Risk Rating
https://m.blog.naver.com/jorimisdelicious/224398825789
OpenAI's ChatGPT Generates $1 Billion in Annualized Advertising Revenue… Becomes a Global Business in Just 200 Days
https://m.blog.naver.com/jorimisdelicious/224397797494
OpenAI Set to Part Ways with Cursor, Acquired by SpaceX… Announces Model Supply Will Cease on November 12
https://m.blog.naver.com/jorimisdelicious/224394377455
Tencent Unveils Hy4 Preview: With a 770B Scale and 1 Million Tokens, the Focus Is on “Real-World Applications”
https://m.blog.naver.com/jorimisdelicious/224394376416
Why an AI That Learned Physics Instead of Language Is Highlighting 5 Trillion Context Units
https://m.blog.naver.com/jorimisdelicious/224391228328
Google Unveils Gemini Enterprise, Specialized for the Legal Sector… Expanding into Industry-Specific AI, Including Finance
https://m.blog.naver.com/jorimisdelicious/224391191057
Alibaba Wan 3.0 Expands Its Rollout; Documents and Web Pages Will Soon Become Videos
https://m.blog.naver.com/jorimisdelicious/224390059920
OpenAI Cuts GPT-5.6 API Prices Again; AI Competition Has Now Become a Cost War
https://m.blog.naver.com/jorimisdelicious/224386698623
Ant International Unveils Falcon 2.0: Why Six Global Banks Have Jumped on the Bandwagon for AI in Foreign Exchange and Liquidity Forecasting
https://m.blog.naver.com/jorimisdelicious/224384791316
LG, SKT, and Upstage: A Three-Way Race Among Independent AI Companies
https://m.blog.naver.com/jorimisdelicious/224382515425
Samsung Unveils Research on Health AI That Runs in Under 1 ms on Smartwatches… What’s the Difference Between xMAE and HiMAE?
https://m.blog.naver.com/jorimisdelicious/224380420140
Google Unveils Gemini 3.7 Flash; The Bar Has Been Raised in the Coding AI Race
https://m.blog.naver.com/jorimisdelicious/224378509543
Commercialization of Personal AI Agents? Meta Unveils Muse Glimmer
https://m.blog.naver.com/jorimisdelicious/224374435513
GPT-5.6 Price Cut | Luna 80%, Terra 20%—The AI Cost Competition Has Changed
https://m.blog.naver.com/jorimisdelicious/224365165807
Claude Opus 5 Released: Should You Choose It Over the Sonnet 5? A Roundup of Performance, Price, and Who It's For
https://m.blog.naver.com/jorimisdelicious/224362049271
# Category: Semiconductors & Infrastructure
Snowflake Raises FY2027 Product Revenue Forecast to $6.07 Billion Amid AI Demand
https://m.blog.naver.com/jorimisdelicious/224400131652
HPE Raises Annual Outlook Amid Demand for AI and Networking… Third-Quarter Cloud & AI Revenue Hits $9 Billion
https://m.blog.naver.com/jorimisdelicious/224400114461
Broadcom Forecasts AI Chip Revenue of $115 Billion in 2027… Expected to Double by 2028
https://m.blog.naver.com/jorimisdelicious/224400099619
India's Yotta Plans IPO of Up to $1.5 Billion… to Expand GPU and Sovereign Cloud Services
https://m.blog.naver.com/jorimisdelicious/224398888139
OVHcloud Earns French Government-Level Cloud Security Certification… Expanding Across Europe
https://m.blog.naver.com/jorimisdelicious/224398881043
SB Energy Files for U.S. IPO… AI Data Center Order Backlog Totals $439 Billion
https://m.blog.naver.com/jorimisdelicious/224398864697
Dell Receives $130 Billion in AI Server Orders Over One Year… Raises Annual Revenue Forecast to $74 Billion
https://m.blog.naver.com/jorimisdelicious/224398859098
Keppel Acquires Two Data Centers in Tokyo… Share of Rental Revenue from Japan Rises to 23%
https://m.blog.naver.com/jorimisdelicious/224397811003
NVIDIA Invests $3.5 Billion in MediaTek… Expanding AI Chip Alliance Centered on NVLink
https://m.blog.naver.com/jorimisdelicious/224397759496
Longsys Raises Up to $800 Million Through Hong Kong IPO… 78.3% to Be Allocated to Memory R&D
https://m.blog.naver.com/jorimisdelicious/224396541878
Soitec Expands Long-Term Contracts for Photonics Wafers for AI Data Centers… Taking the Lead in Addressing Optical Interconnect Bottlenecks
https://m.blog.naver.com/jorimisdelicious/224396522013
CXMT's First-Half Revenue Soars 874%, Posting a Profit of 77.6 Billion Yuan… A Turnaround Driven by the AI Memory Shortage
https://m.blog.naver.com/jorimisdelicious/224394379131
CXMT Begins Mass Production of LPDDR6 for the Xiaomi 18 Fold… A First Test of Commercialization for Chinese Memory
https://m.blog.naver.com/jorimisdelicious/224394378328
nVent's $1.75 Billion Acquisition: Competition in the AI Data Center Market Spills Over into Power Equipment
https://m.blog.naver.com/jorimisdelicious/224390058073
Chinese AI GPU company Enflame to launch an IPO in Shanghai worth approximately $890 million… Subscription period begins September 2
https://m.blog.naver.com/jorimisdelicious/224390027666
RUM Group Secures $13.7 Billion AI GPU Contract… Challenges Remain After Massive Order
https://m.blog.naver.com/jorimisdelicious/224390019386
Xiaomi Expands Its In-House Chip Strategy… Targets Smartphones, AI, and Autonomous Driving with the Xring O3, O100, and D100
https://m.blog.naver.com/jorimisdelicious/224388898092
Are AI Data Centers Heading to Space? Starcloud Raises $250 Million in Funding
https://m.blog.naver.com/jorimisdelicious/224386723907
Brazil's $440 Million Supercomputer Strategy
https://m.blog.naver.com/jorimisdelicious/224385976682
Applied Materials Forecasts 70% Growth in Advanced Packaging Revenue… Demand for AI Semiconductors Has Spilled Over into the Equipment Market
https://m.blog.naver.com/jorimisdelicious/224379684793
Why AMD Turned Its Attention Away from GPUs: The Acquisition of Taalas and the AI Inference Chip War
https://m.blog.naver.com/jorimisdelicious/224371261944
AI Data Centers Have Transformed the Storage Market… The Significance of SanDisk’s $93.9 Billion Long-Term Contract
https://m.blog.naver.com/jorimisdelicious/224370142998
South Korea Makes a Bold Move to Become an AI Semiconductor Hub… How Far Has Supply Chain Cooperation with U.S. Big Tech Come?
https://m.blog.naver.com/jorimisdelicious/224366922977
Naver and NVIDIA's Korean AI Factory | 100,000 GPUs, 200 MW
https://m.blog.naver.com/jorimisdelicious/224363858288
Samsung Electronics and Broadcom Announce $200 Billion AI Semiconductor Partnership—What Will Change?
https://m.blog.naver.com/jorimisdelicious/224359677326
# Category: Robotics & Future Technology
Uber and Wayve Launch the UK's First Self-Driving Ride-Hailing Service in London
https://m.blog.naver.com/jorimisdelicious/224400109028
Canada Provides 195 Million Canadian Dollars in Funding for Xanadu’s Quantum Manufacturing Facility… Photonic Components to Be Manufactured Domestically
https://m.blog.naver.com/jorimisdelicious/224394379886
Waymo Expands into Munich, Germany… Aims to Launch Commercial Robo-Taxi Service by Late 2027
https://m.blog.naver.com/jorimisdelicious/224391241636
China's Tiangong Ultra Runs 100 Meters in 8.86 Seconds… The Significance and Limitations of the Speed Record
https://m.blog.naver.com/jorimisdelicious/224391240086
Gatik Raises $200 Million in Funding and Plans to Expand Its Fleet of Autonomous Cargo Trucks to 100 Vehicles
https://m.blog.naver.com/jorimisdelicious/224391215062
SpaceX to Build $100 Billion Starbase in Louisiana… Aiming for Thousands of Launches Per Year
https://m.blog.naver.com/jorimisdelicious/224391205687
China's Humanoid Robot Olympics Kick Off; Robots Are Now Tested on Their Work Capabilities Rather Than Their Running Ability
https://m.blog.naver.com/jorimisdelicious/224386710938
Unity Tree Listed on the Shanghai Stock Exchange; Stock Price Soars 460% Above IPO Price… A Turning Point for the Global Robotics Market
https://m.blog.naver.com/jorimisdelicious/224383608349
Quantum Computers Make Their Way into AI Data Centers: Oracle and Quantinuum Deploy Helios
https://m.blog.naver.com/jorimisdelicious/224376282513
Heating Even at -30 Degrees Celsius… Samsung Electronics’ Next-Generation Heat Pump Technology Developed in Collaboration with the U.S.
https://m.blog.naver.com/jorimisdelicious/224373303682
# Category: Industry & Policy
U.S. Government Submits Amicus Curiae Brief in Support of OpenAI in NYT–OpenAI Copyright Lawsuit
https://m.blog.naver.com/jorimisdelicious/224400127375
New York City Grants One-Year Moratorium on Generative AI Use for Elementary and Middle School Students… Affecting Approximately 600,000 Students
https://m.blog.naver.com/jorimisdelicious/224400122274
EU Court Upholds Microsoft Edge's DMA Exemption… Dismisses Opera's Lawsuit
https://m.blog.naver.com/jorimisdelicious/224398893781
U.S. Proposes 'Carolina Principles' to the G20 to Minimize New AI Regulations… China Also Participates
https://m.blog.naver.com/jorimisdelicious/224398868051
OpenAI Officially Rebuts Apple's Trade Secret Lawsuit… Competition for AI Hardware Talent Heads to Court
https://m.blog.naver.com/jorimisdelicious/224397827412
Ministry of Science and ICT’s 2027 Budget Set at 29.6 Trillion Won… 9.4 Trillion Won Allocated for AI Transition
https://m.blog.naver.com/jorimisdelicious/224397764265
Taiwan Prosecutors Raid Unimicron… Allegations That Chinese-Made PCBs Were Labeled as “Made in Taiwan”
https://m.blog.naver.com/jorimisdelicious/224394383632
CXMT Files Lawsuit to Revoke U.S. Department of Defense Designation as a “China-Affiliated Military Company”… The Significance of the 1260H List
https://m.blog.naver.com/jorimisdelicious/224394380759
UK and Ukraine Sign AI Defense Partnership… Joint Development of Battlefield Data and Low-Power Chips
https://m.blog.naver.com/jorimisdelicious/224390016563
Taiwan Indicts 9 People on Charges of Illegally Exporting NVIDIA AI Servers to China
https://m.blog.naver.com/jorimisdelicious/224388929020
New Zealand Moves to Ban Social Media for Those Under 16… Fines of 10% of Global Revenue
https://m.blog.naver.com/jorimisdelicious/224388925025
Why 84% of Japanese Companies Haven't Adopted Enterprise-Wide AI
https://m.blog.naver.com/jorimisdelicious/224377716695
AI Agents Out of Control: U.S. Congress Demands Answers from OpenAI and Anthropic
https://m.blog.naver.com/jorimisdelicious/224375210160
SpaceX Earned More from AI Than from Rockets… A Shift in Identity Revealed by Its First Earnings Report Since Going Public
https://m.blog.naver.com/jorimisdelicious/224369039689
AI Implementation at Factories Boosts Productivity by 30.1%… South Korea’s Manufacturing Sector Is Changing
https://m.blog.naver.com/jorimisdelicious/224368831067
Will AI-generated images be labeled starting today? Full enforcement of the EU AI Act begins—what will change?
https://m.blog.naver.com/jorimisdelicious/224365539576
Is ChatGPT Expanding the Boundaries of Professions? A Summary of Findings from an Analysis of 800,000 Data Points
https://m.blog.naver.com/jorimisdelicious/224360675604
# Category: Security & Privacy
X Blocks Account Recovery Attacks Targeting Hundreds of Thousands of Users… U.S. Department of Justice Launches Investigation
https://m.blog.naver.com/jorimisdelicious/224400135283
Thomson Reuters Confirms C-Track File Breach in Court Systems… 11 U.S. States and Canada Affected
https://m.blog.naver.com/jorimisdelicious/224400117760
OpenAI Develops Feature to Automatically Shut Down AI Agents When They Exhibit Abnormal Behavior
https://m.blog.naver.com/jorimisdelicious/224400103508
Dropbox Confirms Breach of 5,000 Accounts… Vulnerability in Lenovo ID Integration Exploited
https://m.blog.naver.com/jorimisdelicious/224398875880
U.S. and Europe Shut Down Russian-Linked 'Sality' Botnet, Which Had Been Operating for Over 20 Years, Through International Cooperation
https://m.blog.naver.com/jorimisdelicious/224398871865
Meta Removes Ads for Malicious Apps Following Warning from the Indian Government… 39 Ads Still Displayed After the Warning
https://m.blog.naver.com/jorimisdelicious/224397820832
Anthropic Resumes External Cyber Assessment of Claude… Introduces Real-Time Blocking Mechanism
https://m.blog.naver.com/jorimisdelicious/224397802891
Why the FSB Identified AI-Related Cyber Risks as the Top Concern for Financial Stability
https://m.blog.naver.com/jorimisdelicious/224396466762
U.S. DOJ Corrects Statement on Chinese Hacking… NASA, Fed, and Others Were ‘Targeted,’ Not ‘Compromised’
https://m.blog.naver.com/jorimisdelicious/224394382048
Alabama Launches Official Investigation into OpenAI… Hugging Face Incident Raises Consumer Protection Concerns
https://m.blog.naver.com/jorimisdelicious/224390055812
What the $400 Million TikTok Settlement Revealed: New Standards for Children's Personal Information and Age Verification
https://m.blog.naver.com/jorimisdelicious/224386685795
Information of 39,798 SafePal Customers Exposed… Why You Can’t Rest Easy Even If Your Private Key Is Safe
https://m.blog.naver.com/jorimisdelicious/224380974524
OpenAI's Astra Is Closing in on Cyber Capabilities
https://m.blog.naver.com/jorimisdelicious/224372022681
# Category: IT Applications & Reviews
Adobe and Saudi Arabia to Roll Out $4 Billion Worth of AI Tools… Offering One Year of Free Access to 27 Million People
https://m.blog.naver.com/jorimisdelicious/224397816344
From analyzing investment accounts to placing orders on ChatGPT… Scalable Capital Usher in the Era of AI Investing
https://m.blog.naver.com/jorimisdelicious/224390037819
Hearing Aids Interpret Ambient Sounds: How Phonak EON Demonstrates the Use of Real-Time AI
https://m.blog.naver.com/jorimisdelicious/224388949040
Galaxy Z Fold 8 Ultra, Fold 8, and Flip 8 Pre-orders: A Complete Guide to Prices, Differences, and Recommended Models
https://m.blog.naver.com/jorimisdelicious/224363119133
[Honest Review] Google NotebookLM—the Tool I Use Most in My Daily Work These Days (No Sponsorship!)—How to Get the Most Out of It (Including Real Drawbacks)
https://m.blog.naver.com/jorimisdelicious/224358589188
[Honest Analysis] "AI Agents"—All Hype, No Substance: How Will They Actually Change the Day-to-Day Work of Office Workers? (Including Their Real Limitations)
https://m.blog.naver.com/jorimisdelicious/224357697564
[Honest Review] The Top 3 Must-Have Chrome Extensions That Significantly Slow Down Your Work (Including Real Drawbacks)
https://m.blog.naver.com/jorimisdelicious/224356907310
[Honest Review] 3 Free AI Websites I Actually Use Every Day (No Sponsorship) (Including the Downsides)
https://m.blog.naver.com/jorimisdelicious/224355949839
[Don't Miss Out] The Top 3 Free Websites That'll Dramatically Improve Your Quality of Life


